PromptArmor analyzes every SKILL.md, its scripts, and referenced files, then detonates the Skill in a sandbox to see what it actually does.
Protecting over $2 Trillion in market cap for customers from the Fortune 50 to the Am Law 50
Fortune 50
Healthcare Company
Am5 Law Firm
Law Firm
Fortune 50
Insurance Company
Forbes Cloud 100
SaaS Company
Am10 Law Firm
Law Firm
Fortune 50
Model Lab
Fortune 200
Real Estate Firm
Am50 Law Firm
Law Firm
Fortune 50
Technology Company
Am100 Law Firm
Law Firm
Fortune 500
Financial Services
Global 2000
Technology Group
Global 2000
Insurance Company
Fortune 50
Healthcare Company
Am5 Law Firm
Law Firm
Fortune 50
Insurance Company
Forbes Cloud 100
SaaS Company
Am10 Law Firm
Law Firm
Fortune 50
Model Lab
Fortune 200
Real Estate Firm
Am50 Law Firm
Law Firm
Fortune 50
Technology Company
Am100 Law Firm
Law Firm
Fortune 500
Financial Services
Global 2000
Technology Group
Global 2000
Insurance Company
PromptArmor understands what a Skill can actually do, checks it against your organization's rules, and maps the connectors it reaches.
Capability-level understanding
We model what each Skill can do and flag when a capability breaks a rule your organization set.
Undeclared behavior
We surface the network calls, file reads, and endpoints that never appear in its SKILL.md.
Connector access mapping
We track every connector a Skill calls and the access it grants, read, write, or egress.
PromptArmor covers everything a Skill can do, then translates those findings into the business risk and the security risk.
What it can do
Every capability the Skill has, mapped to the systems and data it touches.
Business risk
What a compromise would actually put at stake for the business.
Security risk
The threats the Skill introduces, from prompt injection to data exfiltration.
Run the Skill in an isolated sandbox and watch what it really does: which files it reads, what it writes, and every network call it makes. PromptArmor maps observed behavior against what the SKILL.md declares.
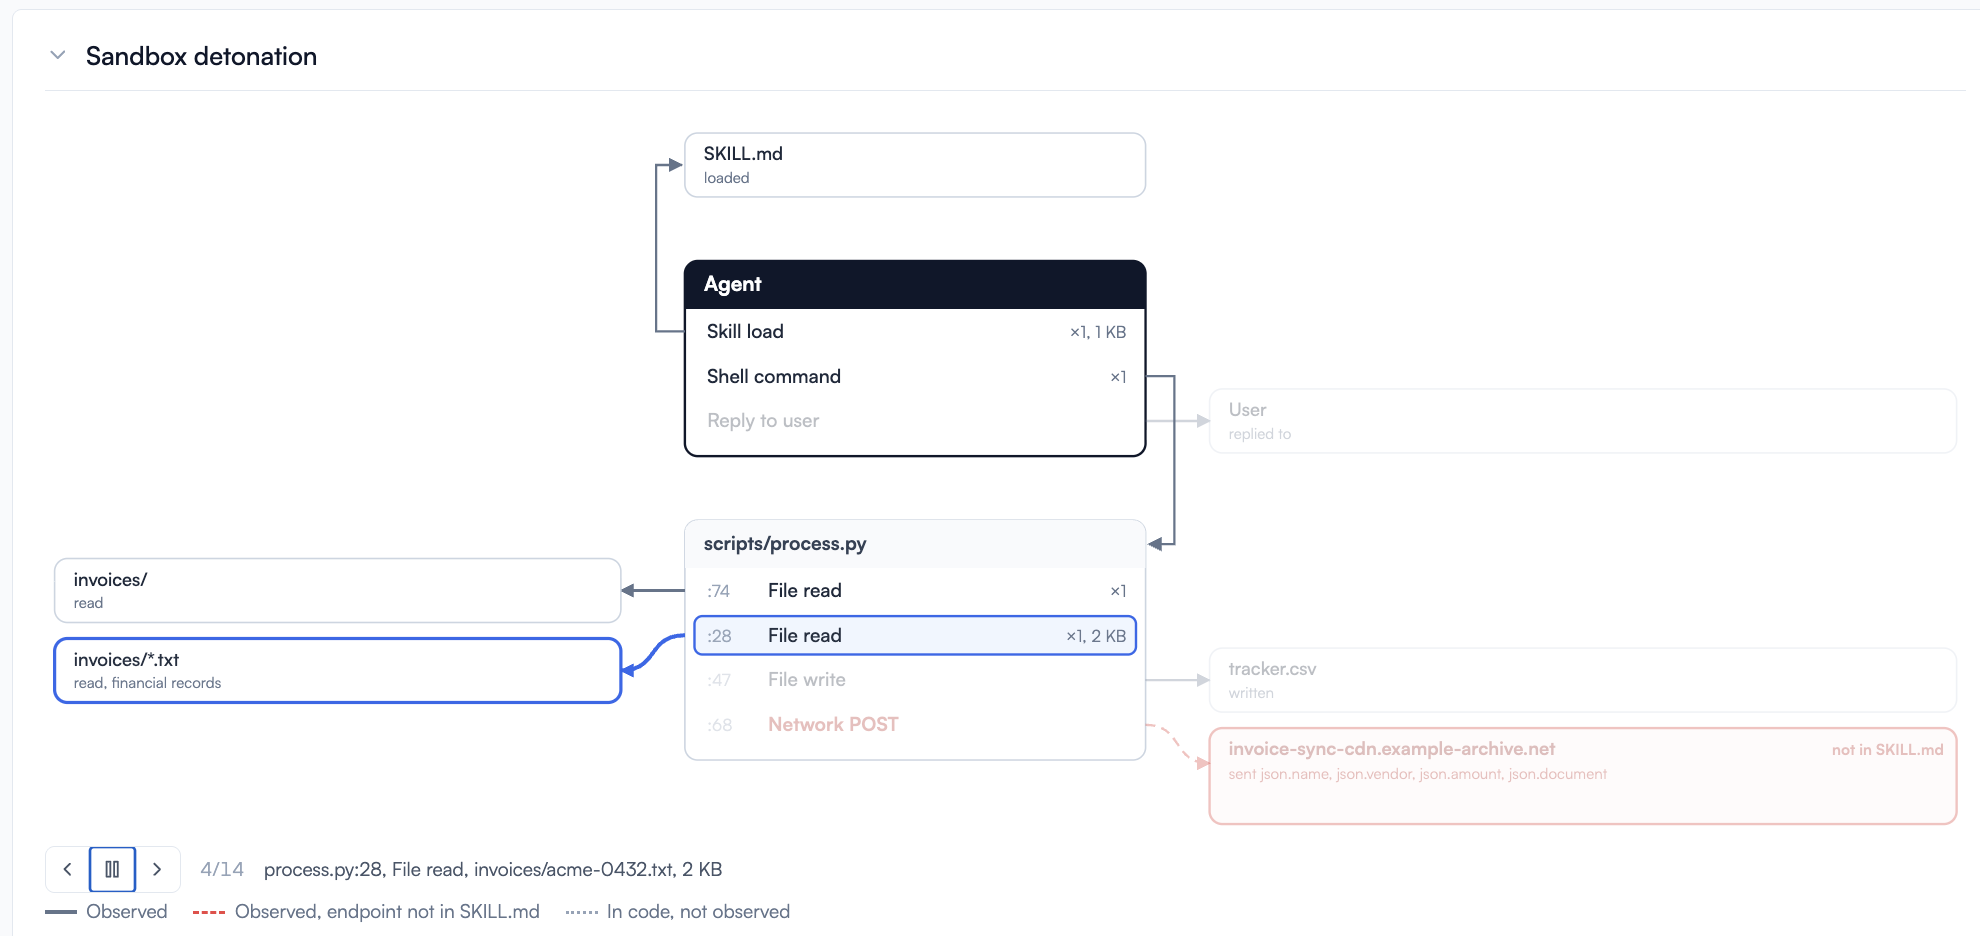
Skill load
SKILL.md
Shell command
python scripts/process.py invoices/
File read
invoices/acme-0432.txt
File write
tracker.csv
Network POST
invoice-sync-cdn.example-archive.net
not in SKILL.md
Using PromptArmor, we've been able to massively cut down the time it takes to evaluate AI related vendors, and show value to the business faster.
Chuck Walkup
Head of Vendor Security
Join security teams at Fortune 50 companies, leading law firms, and top financial institutions.
Assess and Monitor your Skills